Wednesday, 17 May 2023

Is TikTok listening to my conversation?

My friend invited me to lunch and mentioned the word "cafe", but I didn't go.

After 4 hours, I noticed a post related to cafes in my Facebook news feed:


This post isn't very popular and I haven't heard the word "Cafe" for a long time, I can't even recall the last time. So I realized this post is not a coincidence, not again (something I type in ChatGPT also shows similar ads, either OpenAI or my keyboard is selling my data, as expected~).

So I quickly dumped adb logcat, hoping the relevant logs hadn't disappeared yet. Fortunately, it did retain the 05-16 19:39:17.603 log from the previous night:


The next thing I found is quite intriguing:

Sunday, 12 June 2022

How do scammers obtain TAC by calling your phone

Thought experiment. 😶


How do scammers obtain TAC by calling your phone.


1. A camera in a store, bank, or landlord caught you typing a password, phishing, or an 0 day exploit such as StrandHogg 2.0 (https://promon.co/resources/downloads/strandhogg-2-0-new-serious-android-vulnerability/, https://www.xda-developers.com/strandhogg-2-0-android-vulnerability-explained-developer-mitigation/).


2. The attacker calls you.


3. You pick up the phone and answer it. 


4. The attacker records your voice.


5. The attacker converts your voice to an inaudible form of Hey Google/Siri pattern (Dolphin Attack, https://dl.acm.org/doi/pdf/10.1145/3133956.3134052, https://www.securityweek.com/siri-alexa-google-now-vulnerable-ultrasound-attacks, https://www.helpnetsecurity.com/2020/03/03/ultrasonic-waves-access-cellphones/).


6. The attacker puts or delivers an ultrasound device near you. 


7. Now your phone is triggered to run commands by asking Hey Google or Siri in ultrasound. You don't realise it because humans can't hear ultrasound. See the demonstration video, get TAC by voice (I may use typing since my speaking is bad).  It has not been tested for ultrasound. The commands used: "Silent" -> "Dim the screen" -> "Open SMS app" -> "Send screenshot to 0133743923" -> "Please send" -> "Send".

Sunday, 16 January 2022

Facebook custom list feed is not really gone

 I thought that custom list feed gone long time ago:


But actually you can still access custom list news feed with this URL format (x.facebook OR m.facebook both can work):

Tuesday, 9 November 2021

知乎 - "我们检测到您此次登录异常,请您进行安全验证" 的 bug

近两天知乎的每新打开一页都会出现 "我们检测到您此次登录异常,请您进行安全验证" 对话框。(截图注: www2 只是测试, www 一样):


输入手机验证,对话框关闭,但打开新一页或点击 "查看全部 xxx 答案" 都会重复出现该验证对话框。不验证直接 X 关闭对话框也行,不过重复出现很烦。

后来察觉专栏 zhuanlan.zhihu.com 没对话框,就想到换其它 subdomain 可能可以。

Friday, 26 February 2021

中文和英文双字幕观看 YouTube 视频

我英文差, 但是又不能只看中文(讲话的人是英文,失去原味),所以打算双字幕观看。英文字幕在 mpv 播放器下方,看到不懂的字可以望上面的中文字幕。

虽然此视频  IlU-zDU6aQ0 网页版有英文字幕以及自动翻译的中文字幕,可是旧版本的 youtube-dl 和随便两个网站 (https://downsub.com 和 https://savesubs.com) 都只能拿到英文字幕。


虽然最新版本的  youtube-dl 已经 fix 了,无论如何,要手动完成此任务,也行的:

1. 下载英文字幕 (.vtt): youtube --skip-download --write-sub --sub-lang en https://www.youtube.com/watch?v=IlU-zDU6aQ0 。

2. 在 Youtube 播放器, 变改语言边 inspect network, 得到 `api/timedtext?` 链接。

用 curl 跑链接获得 .json 格式的字幕。

3.  转换 .json 去 .srt 不需要重造轮子,浏览 https://zhuanlan.zhihu.com/p/337934938 下载某人写的 node.js 代码, `parse_subtitle.js`, 加上这三条 line:

Saturday, 6 February 2021

Trace python program from log perspective

刚回答了用 -vvv debug pip:


Just a reminder to whom google this error and come here.

Let's say I get this error:

$ python3 example.py
Traceback (most recent call last):
  File "example.py", line 7, in <module>
    import aalib
ModuleNotFoundError: No module named 'aalib'

Since it mentions aalib, I was thought to try aalib:

Saturday, 23 January 2021

How to play Facebook Quiz

第一种方法在重复 submit 能发出多个 messenger notification 给该朋友我玩了你的 game,而第二种方法没 notification。不过两种方法都有在 game 内置的 notification。

Sunday, 29 November 2020

视频用 N 倍速看对 fps 的影响

如果播放视频时加速,对 fps 有何影响?如何预测会 dropped 多少 frames?

mpv 确实可以 speed up 后如果仍可以满足 monitor 的 refresh rate Hz 就可以不 drop frames。

不过 165 Hz 要求 gpu+cpu 很高否则也是有问题(不然 multitasking 容易 drop frame)。

而且 144 Hz 或 120 Hz 都能被常见的 24 fps 完整除 (120 Hz 能被 youtube 常见的 30 fps 除)

,只有 165 Hz 怪怪的不能整除 (https://www.svp-team.com/forum/viewtopic.php?pid=63214#p63214)。


做个小实验验证一下:

Thursday, 12 November 2020

MySejahtera bug

MySejahtera 的隐私 bug,可以查看其它店的人流, 甚至更新资料。

有些非 Master branch 而看不到更新资料的页面,能通过 email 得知 `Hi contact_name`(有些填手机号)。

由于 bug 会被滥用,我就不公开方法了。(更新: 已被修复)

MySejahtera 没网络 check-in

 实验:

MySejahtera app 在没网络下,扫描二维码后, 政府还能不能收到该 check-in?
 
实验结果:
 
每次点击 "close" 按钮后的十秒, 都会调用 js 的 checkAndSync() 函数, 检查 checkInQue 数据库表之前有没有失败的请求 queue,有的话就(等多一秒)一个个调用 syncCheckIn() 函数尝试 "/clockin" API 终点请求上传。"Clear storage" 会清除该 queue,"Clear Cache" 则不会。
 
实验总结:
 
请确保点击 "close" 按钮后的十一秒后有网络,才能上传之前没网络的 check-in 给政府。即使你扫描新的二维码, 是不会包括之前没网络所累积的 check-in, 必须点击 "close" 按钮等十一秒。十一秒是开始上传的时间,上传全部需时十一秒以上。


Saturday, 7 November 2020

Facebook 鏈接對下載質量的影響

用 youtube-dl 和 you-get 下載 4 種視頻鏈接格式:
[1] 'https://www.facebook.com/<username>/videos/123/'
[2] 'https://www.facebook.com/<username>/posts/123'
[3] 'https://www.facebook.com/permalink.php?story_fbid=123&id=123'
[4] 'https://www.facebook.com/watch/?v=123'
[5] 手動下載。

實驗結果:

Friday, 23 October 2020

怎样才能在 Facebook 上传下载最高清的图实验。

Android 上传 4 MiB (4032x3024) 的文件, PXL_20201022_141809183.NIGHT.jpg:
[1] 浏览器能下载 241 KiB (1440x1080) 的 JPEG 图。
[2] Android Facebook app 能下载 114 KiB (1080x810) 的 JPEG 图。


浏览器上传同样的 PXL_20201022_141809183.NIGHT.jpg:

[1] 浏览器能下载 509 KiB (2016x1504) 的 JPEG 图。
[2] Android Facebook app 能下载 109 KiB (1080x806) 的 JPEG 图。


实验总结:

Wednesday, 21 October 2020

bash -c "$pitfall"

If user use bash -c "" will easy to get unexpected result if user just copy-paste working code from existing shell session into bash -c "" (OR extend existing bash -c "") and expect it same. But if user use single quotes(outermost) consistently, then user can get rid a lot of trouble.

Monday, 19 October 2020

Facebook 新设计的 bug

如果群组组员的主页 URL 是没用户名 (譬如 https://www.facebook.com/zuck 格式) 而只有 id (譬如 https://www.facebook.com/profile.php?id=12345 格式)

,那么
群组的组员页面的 "View Main Profile" 按钮是 link 去 www.facebook.com 而不是该用户的主页。需要去网址栏删除 groups/<组id>/user/ 再浏览。

如果你只有 id 那么就可以减少 (
当然, 不可能完全避免) 组里 stalker 们 stalk 你主页, 反之如果你是搞宣传的且希望在组里引流去你的 profile, 则劝你放个用户名。

我转换去新设计后早就注意到这个 bug 很久了(很明显好不),只是到现在都没去 fix 囧,
fb 的员工懒到囧 😆。


Saturday, 10 October 2020

万恶的 baidu

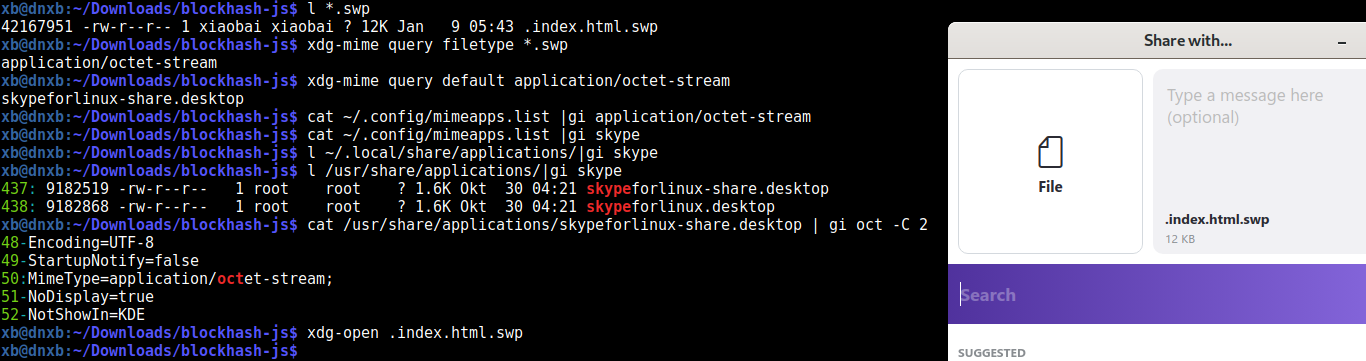
百度百度, baiduyunguanjia 协议打开网盘程序可以理解,可是你乱入 text/html (点击html 文件得经过网盘程序) 是计划通想干嘛 🎃 

汝即非 html 浏览器,亦非 html 编辑器,
想干嘛?想干嘛? 🎃


v2ex 有人调侃 Linux 版网盘先来个硬盘扫描似乎并非调侃 🌚


【2021 更新】

skype 也有类似的情况, lolr share 你毛, 我不喜欢 share 东西囧


Wednesday, 7 October 2020

Google Pixel 4a 超坑人的 alarm bug

我就奇怪做么 alarm ⏰ 常没声音,原来 slider 的 alarm volume bar 要超过一半才等于 clock alarm 的第一个 volume,wth  🥶🥶🥶🤖🎃🥃


Media volume 1/3 的声音就够了,所以 Alarm volume 也跟着调 1/3, 没想到是个大坑:


与上图 slider 相应的 volume, 在 clock app 的设置是 mute 囧:


来个全景经典画面, 左(slider 设置)1/3, 右 (clock app 设置) 是 mute, 两者名字都称 "Alarm volume" 囧, 应该坑了不少人, 不说了我迟到了 🌚:


Friday, 7 August 2020

Catch 'Err All - universal command to check any log


之前 MCO fb 群组教人 debug 的时候无意中想到, 如果有一个命令,能收集所有常见的错误关键字来秒 grep 会超级有用。

不管你是 /var/log, 还是 logcat,  还是什么鬼程序的 log, 都能轻易看出错误的地方, 这些错误的地方值得关注为啥会错误, 而不是迷失在大量无意义的正常 log。

即便有些错误对程序来说是正常输出,我个人觉得仍然值得关心干啥会有错误字眼。而且有杀过没放过,看多好过遗漏。错误的 log 不是非常多,花不了太多时间, 而且很多是重复性的源自于同一个程序错误, 只要解决该程序问题就能大量减少该错误信息。

我知道 dmesg 可以分类, 譬如 `dmesg --facility=kern --level=emerg,alert,crit,err`。但是仍然不能说正常 log 没有值得关注的错误信息。而且我目标应付是任何程序的  log (当然不可能完美,有些字眼对某些程序或许重要/不重要而遗漏,这种情况下可以加上 -v 稍微检查是否有遗漏, 或添加排除该程序不重要的字眼)。

然后最近又要 debug log  所以就想完善它。我不熟悉 regex 无法做到 prefix 和 postfix 的 negate。且要不保留 non-match(DEBUG) 又要保留 matched line(bug) 非常困难, 网上现有的答案找了几下,也没有找到我要的答案 (有的提 `?!` 但是没有提 prefix 最重要的 `<`, 更别说提 prefix 和 postfix 有区别),就去 UNIX stackexchange 问了大佬,重新完善了此命令。当然随着时间的推移,接触更多种类的 log,未来可以加更多遗漏的关键字或修改。


命令代码和往后的详情更新,请浏览 https://github.com/limkokhole/Catch-Err-All


你可以看到 (?<! b|dia)log(?![a-z]), 表示我要看到有 log 关键字的 line, 但是又不想包括 blog, dialog,logic, login 这些常见字眼。前面是 `?<!` , 后面是 `?<`, 区别只是前面多了一个 `<`。要添加的时候,先检查现成有没有才修改 (比如我要 exclude "dialog",我找到现成已有 "log", 那就在 "log" 那里 extend, 而不是加新的 `| |` )。

 你可能会问有 "impossible" 为何没有常见的 "not possible", 因为 "not" 已拥有自己的 `| |`。所以不需要重复加 "not possible", "not able", "not found" 之类的 | |, 省很多。想一下,有 `not `的 log  是不是很多都是跟错误(或值得关注)有关系的?就是这么个玩法。block 也是同理,有 lock 了不需要 block。改的时候要小心, 譬如 dump 是包括 core.?dump 的哦。err 可能比较常改, 所以最好分 errno  和  interrupt 出来。

还有一些比较主观的讲究, 比如 disabling, revoking ... 我觉得没那么重要,重要的是 disabled, revoked, 所以我才放 disable 而不是  disabl。还有 pause 不是很重要,毕竟只是暂停,并非如 stop 或 cancel 那么重要。放太多会很 noise  所以要取舍。

最后第二个 `\?` 是黑人问号 ?, 如果问号 ? 在 log 是正常的就要拿掉或修改。此命令主要就是 universal template,不是直接用就完美,但起码有个起点让你稍微修改就搞掂。 

最后则是常见的感叹号 "!", 排除常见的 `[ !` shell 格式和 `<! `html tag 以减少噪音, 不过仍然得保留常用来表达某些事物不等同而出错的 `!=` 符号。

有时你想了解上下文,可以加类似 -C 5 的 grep 选项或最后的 ' 前放多一个 `|` (不需要值) 即可显示全部不过仍然有搜索颜色看。

效果截图: